
 1 min read

Multi-Tenant SaaS Architecture and Subscription Billing: A Practical Guide
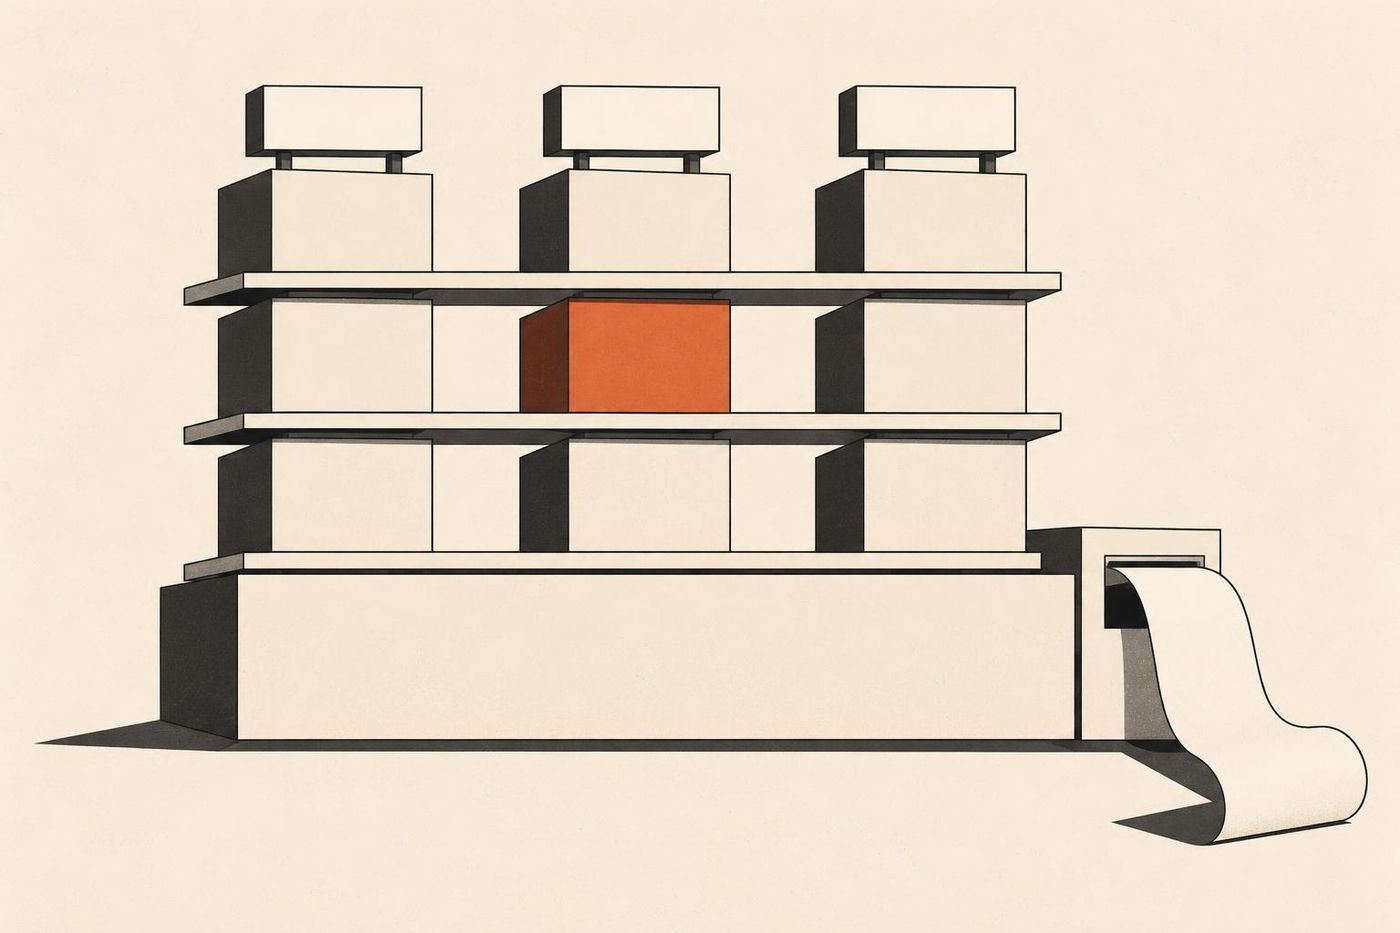
Multi-tenant SaaS architecture lets one application serve many customer organizations while keeping each organization’s data, permissions, and billing boundaries clear. The hard part is not simply sharing infrastructure; it is making tenant context explicit from the first request to the final invoice, without letting convenience erode isolation.
Multi-tenant SaaS architecture is a design in which multiple customer organizations use the same application or infrastructure while their data and access remain logically separated. Subscription billing belongs in that design from the beginning: plans, entitlements, usage, and payment status all need to map reliably to the right tenant.
Start with the tenant boundary, not the billing screen
A tenant is usually a company, team, or account that contains users and shared resources. A user may belong to more than one tenant, so the authenticated user ID alone is not enough to authorize a data request. The application must establish the active tenant and check the user’s membership and role before returning tenant-owned records.
Make that context visible in your application’s core interfaces. For example, pass a validated tenant identifier into repository and service functions rather than relying on a hidden global value:
async function listProjects(tenantId: TenantId, userId: UserId) {
  await requireTenantRole(tenantId, userId, "member");
  return db.project.findMany({ where: { tenantId } });
}
This is not a complete authorization system, but it makes the boundary inspectable. It also helps prevent a common failure: a query that filters by a record ID but forgets to scope that record to the active tenant. For sensitive systems, consider database-level controls as a second line of defense, and test cross-tenant access explicitly.
Write down the isolation model before choosing storage. A shared database with a tenant key is often operationally straightforward; separate schemas or databases can offer stronger separation at the cost of migrations, provisioning, and operations. There is no universal best choice. The right answer depends on regulatory needs, customer expectations, scale, and the team’s ability to operate the design.
Keep subscription state separate from tenant identity
A tenant should exist independently of its subscription. A company may be in a trial, have a past-due invoice, change plans, or cancel while still needing access to export data. Avoid encoding billing status as the tenant’s identity or deleting tenant records when a subscription ends.
Model billing with explicit records: a tenant, a subscription, a plan or price reference, and a history of billing events. Store the payment provider’s identifiers, but do not treat a browser redirect as proof that a payment succeeded. Confirm payment and subscription changes through verified provider events, make event handling idempotent, and record processed event IDs so retries do not create duplicate entitlements.
- Plan: the product and price configuration, including billing interval and currency.
- Subscription: the tenant’s current relationship to a plan, with status and renewal dates.
- Entitlements: the capabilities the application allows, such as seats or feature access.
- Usage: measured activity for metered features, associated with a tenant and a defined period.
Keep these concepts distinct. A successful invoice does not itself explain which buttons should appear in the UI; that is an entitlement decision. Likewise, usage counters should not be inferred from a plan label. For a deeper discussion of serialization boundaries in Rust, see Rust serialization design.
What should happen when billing changes?
Write the lifecycle down as a state transition, then implement it consistently in the backend and interface. For example, a past-due subscription might retain read access while blocking new usage, whereas cancellation might take effect at the end of the paid period. These are product decisions—not universal billing rules—and should be visible to users before they reach the payment screen.
At minimum, decide what happens when a trial expires, a payment fails, a plan changes, a subscription is canceled, or a webhook arrives late. Use timestamps and provider event history to resolve ordering rather than assuming events always arrive in sequence. For metered billing, specify the measurement window, rounding rules, and treatment of corrections. “One active seat” sounds simple until the team must decide whether suspended or invited users count.
Billing pages should make state legible: current plan, renewal or trial end date, usage against limits, and the next action. Use plain language for a payment issue and provide a route to update payment details. A polished interface cannot compensate for ambiguous policy, but good UI can make a clear policy much easier to follow. Teams building a broader account area may also find this guide to customer portal development useful.
Ownership bugs: a game-team example with lessons for SaaS
Tenant isolation is fundamentally about controlling access to shared state. Rust ownership offers a useful mental model for spotting similar boundary mistakes in other software, including games. During a Bevy 0.20 migration, an API or system refactor may change where data is accessed; the safe response is to inspect the actual types and system parameters for the project’s Bevy version, not assume a particular migration changed borrowing rules.
Here is a small, illustrative Rust conflict a game team might uncover while refactoring a system that updates tenant-like player state and then audits it:
fn update_player(players: &mut HashMap<PlayerId, Player>, id: PlayerId) {
  let player = players.get_mut(&id).unwrap();
  player.score += 1;
  audit_all_players(players); // error: immutable borrow while mutable borrow is live
  player.last_updated = now();
}
The mutable borrow of the map remains live because player is used after the audit call. The compiler cannot safely allow the audit function to read the whole map while a mutable reference into it is still active. Trace the problem with a reverse mental model: start at the failing read, ask which mutable references are still alive, then move backward to the code that created them. End the mutable borrow before auditing, or collect the audit data first:
let audit_snapshot = {
  let player = players.get_mut(&id).unwrap();
  player.score += 1;
  player.last_updated = now();
  player.clone()
};
audit_player(&audit_snapshot);
The same habit helps with tenant code: trace every read and write back to the validated tenant boundary, and keep mutable operations narrow. For context on the engine migration itself, read our Bevy 0.20 migration notes. If you are planning an interactive product, explore software development examples and the studio’s project case-study collection.
Make the Rust-to-Svelte boundary deliberate
In a Rust-backed service with a Svelte or SvelteKit interface, the frontend should receive a stable, purpose-built representation of tenant and billing state—not internal database models. Define response types for fields the user may see, such as plan name, usage, limits, and renewal date. Never trust a tenant ID supplied by the client as authorization; derive or validate it on the server for every protected action.
On the UI side, show loading, empty, and error states instead of briefly displaying stale data from a previously selected tenant. When a user switches workspaces, reset tenant-scoped stores and fetch fresh data. This is a small interaction detail with a large security and trust payoff. For teams considering a modern SvelteKit application, see the SvelteKit migration guide and practical software performance considerations.
How UQ applies this
Good architecture work starts with a concrete user flow, then makes boundaries and trade-offs visible during implementation. UniqTech’s relevant services include:
- High-end game development: careful state and ownership reasoning for interactive systems, including Rust-based workflows.
- High-performance software (Rust + Svelte): explicit data contracts between backend services and responsive web interfaces.
- AI-accelerated software development: AI-assisted implementation paired with engineering review, tests, and human validation.
For example, if an AI assistant generates Rust code for a Svelte-facing endpoint and keeps a mutable borrow alive while building a response from the same map, a reviewer can flag the pending borrow conflict before it becomes a build failure. The team can then narrow the borrow’s scope, add a focused regression test, and check that the response still contains only the active tenant’s permitted data. AI can help surface a likely issue; the compiler, tests, and engineer determine whether the fix is correct. Learn more about AI-augmented engineering and how Agile methods support iterative delivery.
A practical decision checklist
- Choose and document the tenant isolation model before adding customer data.
- Require tenant membership and role checks at every protected server boundary.
- Keep subscription records, entitlements, and usage measurements as distinct concepts.
- Make payment-event processing idempotent and resilient to retries or delayed delivery.
- Test that one tenant cannot read, modify, or infer another tenant’s records.
- Design clear UI states for plan limits, payment problems, cancellation, and tenant switching.
Multi-tenant SaaS architecture is strongest when isolation, billing policy, and user experience are designed together. Start with the boundaries, test the failure cases, and keep the decisions understandable to both the people operating the product and the customers paying for it. To discuss a web, mobile, game, or high-performance software project, take the next step with UniqTech.